007 / Work
Security Operations Fabric
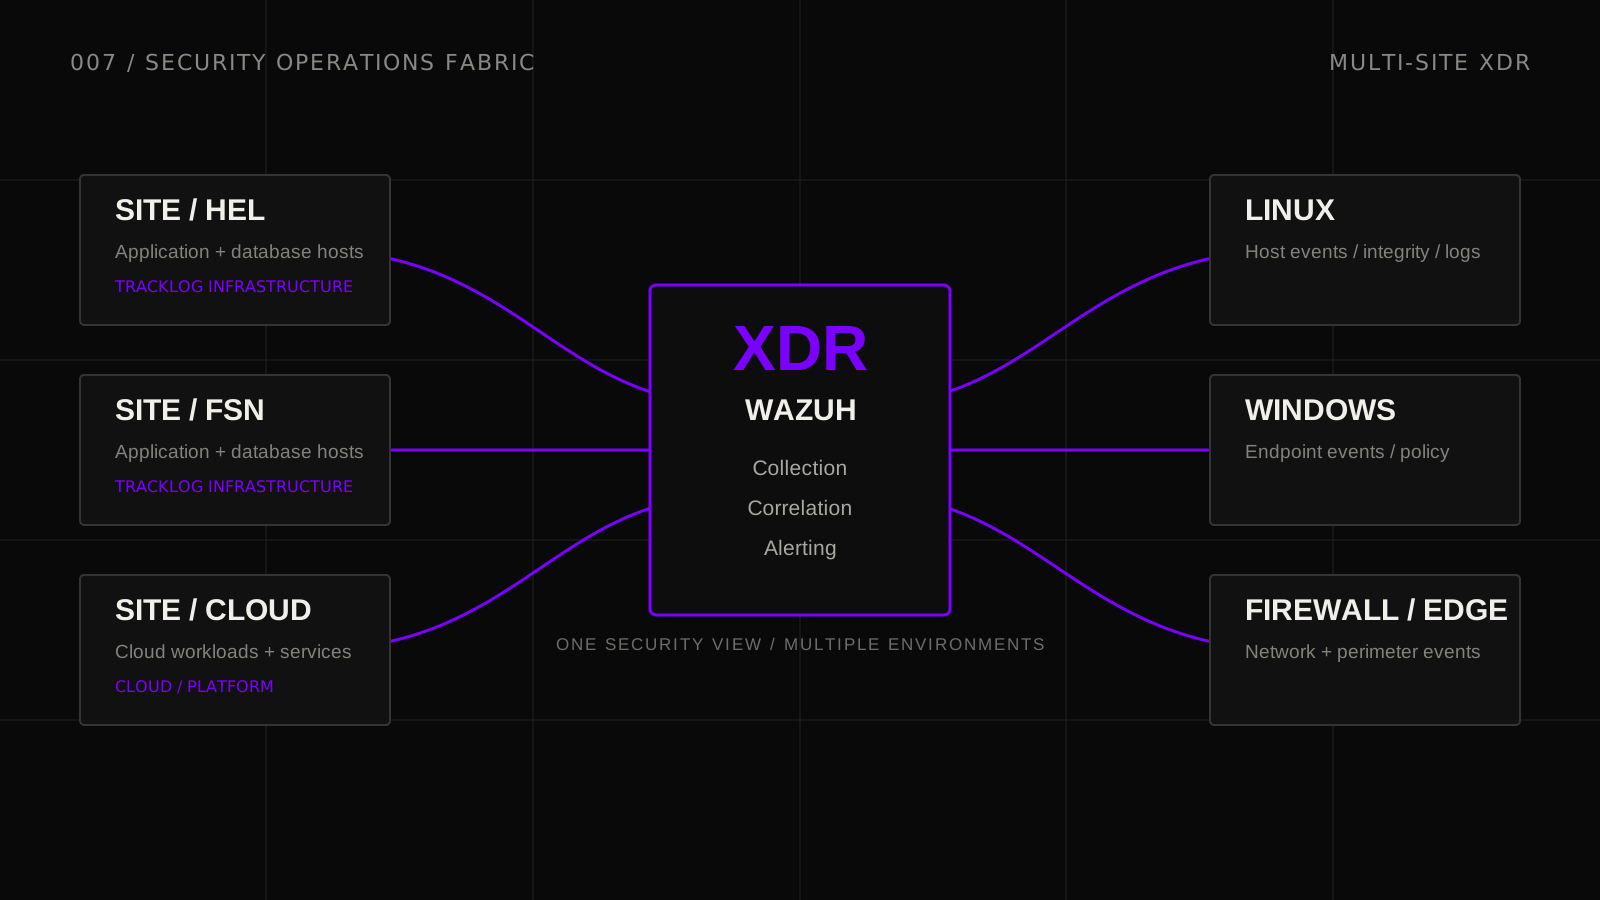
A self-hosted XDR and security-monitoring deployment designed to give one operational view across heterogeneous infrastructure without routing sensitive operational telemetry through a collection of unrelated external dashboards.
The work
Built around
the system.
The work covered the platform as well as the agents: deployment architecture, storage, site and operating-system grouping, endpoint enrolment, firewall log ingestion, alert tuning and the practical job of making security monitoring useful enough that people pay attention to it.
One view across a mixed estate.
The infrastructure spans multiple sites, operating systems and roles. Security events existed in individual hosts and network devices, but there was no single operational layer connecting those signals into a consistent view.
The goal was central visibility without losing control of where the security data lived or turning the deployment into another opaque managed service.
Self-hosted and close to the systems.
We deployed Wazuh as the central analysis and indexing platform, with dedicated storage and network reach to the infrastructure being monitored. Agents were grouped by site, operating system and infrastructure role so policy and investigation could follow the way the estate is actually organised.
That structure matters once the installation moves beyond a handful of endpoints and starts becoming part of day-to-day operations.
Endpoints and the network edge.
Linux application and database servers, Windows systems and firewall events feed the same security plane. That makes host activity, integrity signals and perimeter events available together rather than forcing an investigation to jump between disconnected tools.
The architecture also leaves room to add cloud workloads and additional sites without changing the basic operating model.
Alert less. Mean more.
A security platform that emails everything quickly becomes a platform nobody reads. After rollout, rules and notification behaviour were tightened around meaningful events such as suspicious network activity, host changes and operationally relevant detections.
The aim is not maximum alert volume. It is a security layer that gives the team enough context to decide what needs action.
Next / Start something
Got something
interesting?
Software, hardware, infrastructure or something in between.
[email protected] ↗